Cheap Android Phones Are Shipping With Malware Owners Cannot Delete, Bitdefender Says
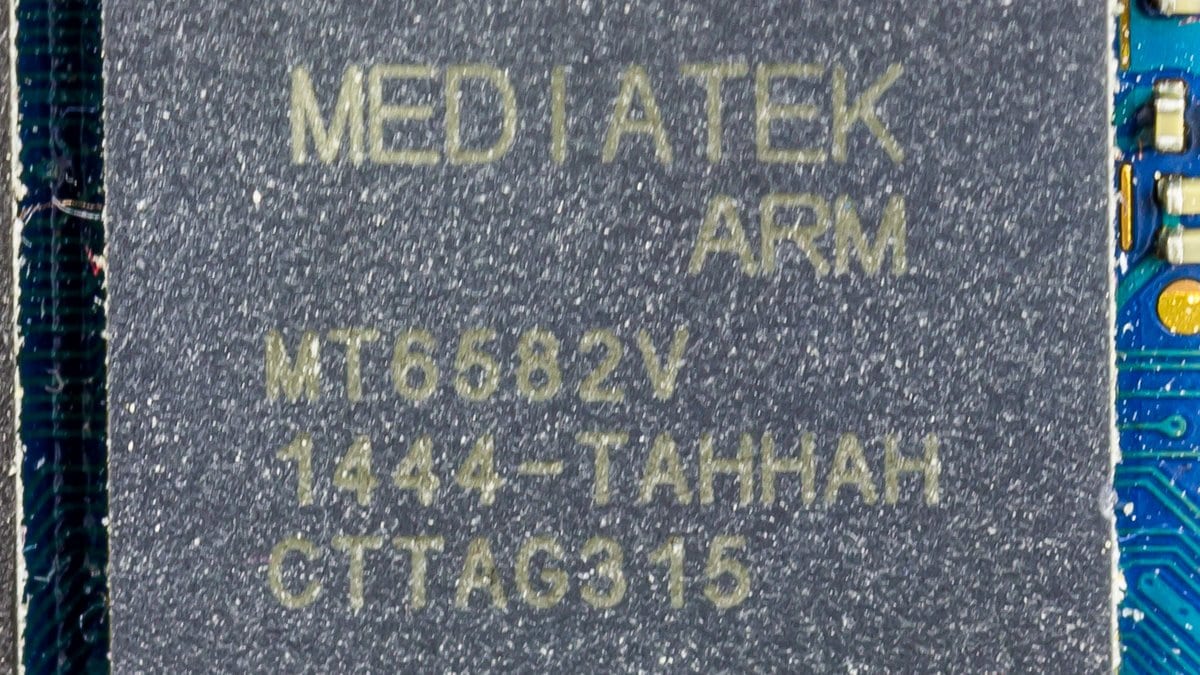
Bitdefender Labs said Oct. 8, 2026, that it had found a hidden app shipping inside the factory software of low-cost Android phones from several brands, all built on MediaTek chips. The company says the app is on the phone before the owner first switches it on, and that the owner cannot uninstall it.
By Bitdefender Labs' account, the campaign, which it calls Midnight Mimosa, is likely designed mainly to make money. Its report says the app quietly installs and removes a changing set of ordinary-looking apps that run invisible advertising fraud, and that it also turns the handset into a relay for other people's internet traffic.
Bitdefender counts at least 32 unique disguised apps, among them fake app locks, weather apps and file managers. Because the app is signed as part of the operating system, the company says it can install software and grant it permissions without prompting the owner. Bitdefender also says it switches off the Google Play Store, which carries Google's on-device scanner, around each installation.
Bitdefender says the same advertising-fraud code turned up in 13 apps distributed by Google Play itself, each with its own signing certificate, across at least two developer accounts. The company describes those as genuine Play builds that passed Google's review.
On that basis the company says it observed the campaign over roughly two years on thousands of devices in more than 150 countries, led by Mexico, France and Italy.
Bitdefender says it can confirm only that certificates bearing the name of a Shenzhen device maker signed firmware on affected phones. The report says it is unclear how those certificates reached the handsets, whether their owner was involved or aware, and where in the supply chain the code is added.
Bitdefender says the app sits in the phone's system partition, so an ordinary uninstall cannot reach it. The report puts the fix with the vendors and marketplaces that ship and sell these phones.