Dutch Cyber Agency Expects Attacks Soon on Two Check Point VPN Flaws
The Netherlands' National Cyber Security Centre, the NCSC, said on Sept. 10, 2026 that it expects attempts to exploit two critical vulnerabilities in Check Point VPN products soon, and advised organizations to install the vendor's updates as quickly as possible.
Check Point had already shipped fixes. Its advisories for the two flaws, CVE-2026-85102 and CVE-2026-85103, were last modified Sept. 9, 2026, and say the problem is fixed and list the packages that carry it. In the NCSC's description, the affected products are the ones organizations use to make secure connections between networks, or for staff working remotely.
In its alert, the NCSC scored both flaws at 9.8 out of 10 on CVSS, the industry's standard severity scale, and said it judges the likelihood of exploitation and the potential damage to be high. Neither flaw requires login credentials, the agency said. One sits in the process that sets up VPN connections, and the other in the handling of certificates, and either can let a remote attacker run code on the system. The NCSC also said that no public proof-of-concept or exploit code has been reported so far, and that it expects attempts at exploitation on a large scale before long. Check Point's advisories carry the same score and mark both issues Critical.
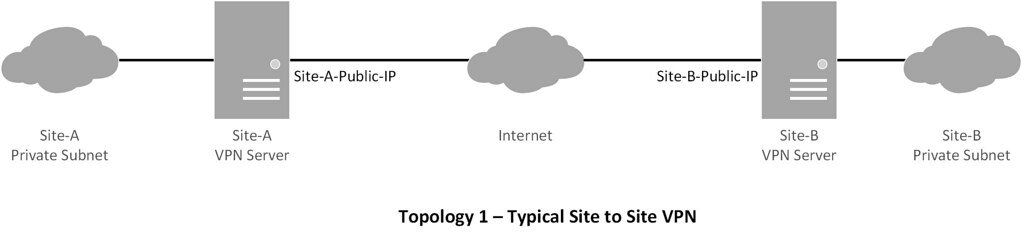
Check Point lists the affected versions as R81.20, R82, and R82.10, along with a set of older releases it marks as end of support, and says R82.20 is not affected. The products involved are its Security Gateway, Security Management Server, and Spark Firewall, where Site-to-Site or Remote Access VPN is in use. For organizations that cannot install the update at once, both the company and the NCSC publish a mitigation for Site-to-Site VPN that restricts which peer addresses can reach the service.
The NCSC advised anyone unsure whether they are running an affected version to ask their IT service provider.