Federal Agencies Have Until Nov. 1, 2026, to Patch an Exploited Cisco Firewall Flaw
Cisco has released fixed software for a flaw in the remote-access VPN of its firewalls that lets an attacker with no credentials reboot the device, and says the flaw is already being used in attacks. The U.S. Cybersecurity and Infrastructure Security Agency added it to its catalog of known exploited vulnerabilities on Oct. 29, 2026, and set a remediation date of Nov. 1, 2026, for federal civilian agencies.
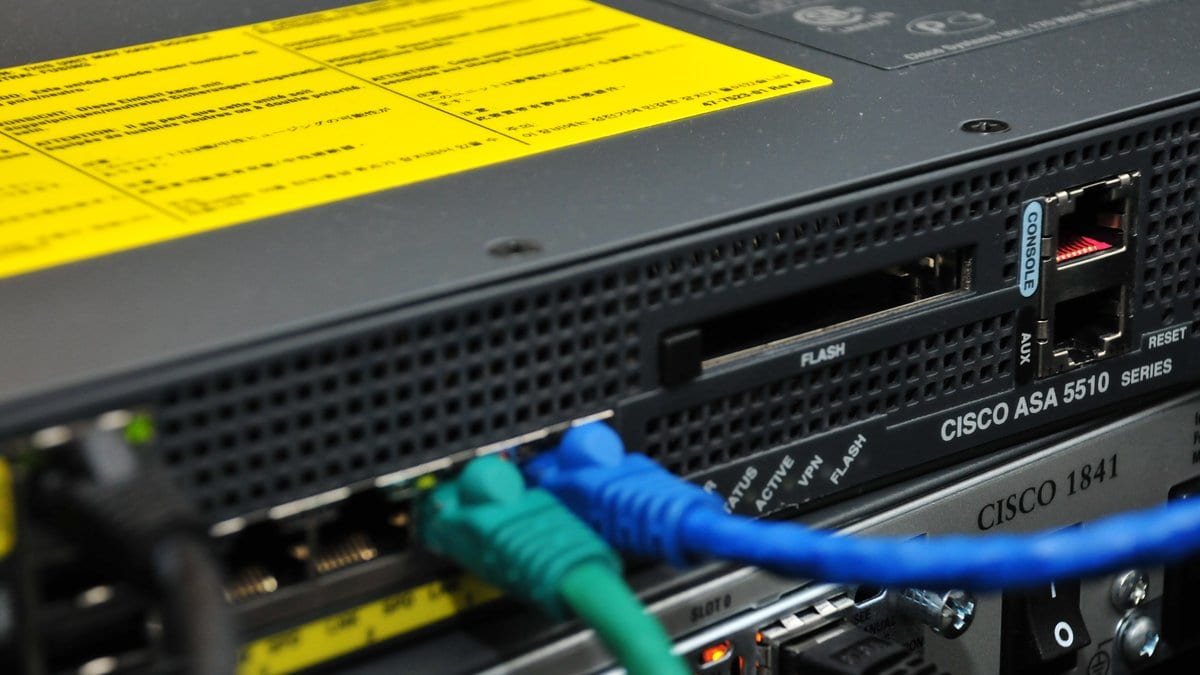
The products affected are Cisco Secure Firewall Adaptive Security Appliance (ASA) Software and Secure Firewall Threat Defense (FTD) Software, the firewalls that terminate the encrypted connections remote staff use to reach an internal network. Cisco's advisory says that a remote attacker without a login can make such a device reload unexpectedly, dropping those connections, that there are no workarounds that address the vulnerability, and that customers should upgrade to a fixed release.
The advisory, cisco-sa-asaftd-tunnel-dos-s6mgkb75, was published Oct. 28, 2026. It tracks the flaw as CVE-2026-76418, rates it High on Cisco's own severity scale with a CVSS base score of 8.6, and names a first fixed release for every affected ASA and FTD version line. A device is affected only if it runs a vulnerable release, its SSL remote-access VPN login service is reachable, and secondary authentication is configured for the tunnel group. Cisco's cloud-delivered firewall products, Secure Access, and Secure Firewall Management Center software are listed as not vulnerable.
Cisco says its Product Security Incident Response Team became aware of active exploitation in October 2026 and does not describe the attacks further. CISA said that it added the flaw on evidence of active exploitation and that its Binding Operational Directive 26-04 requires federal civilian agencies to prioritize rapid remediation of catalog vulnerabilities on publicly exposed assets. Neither names who is exploiting it.
Cisco credits Eric Fernald with finding the flaw during the resolution of a support case.