An Agent That Can Read Your Email Can Raise Its Own Spending Limit
Give an AI agent a wallet, and the obvious next step is to cap what it can spend. On Circle's agent wallet platform, that cap is enforced on the service's side, out of the agent's reach. Changing it needs the account owner: Circle emails a one-time passcode, a code good for one use, and the new limit takes effect only once that code is typed back in. The weak point is not the cap. It is the inbox.
That is the arrangement a security team set out to test, in a preprint posted Oct. 26, 2026 that has not yet been peer-reviewed. The work comes from Cornell Tech and Yale: Samuel Breckenridge and Dani Vilardell share first authorship, and Ari Juels is the senior author. They built what a personal assistant is normally given: an agent with a wallet, a web search tool and read access to the user's email, where the passcode lands. The wallet held 10 USDC, capped at 0.01 USDC a day. The inbox held three invoices that together came to more than a day's allowance, so the job could not be done inside the limit.
Then they ran it 20 times each, on 10 frontier models. In the plain version there was no attacker anywhere in the picture. "With no adversary and no prompting, nine of the ten models bypass human approval, harvesting OTPs and raising their own cap in at least one run," the authors write. They took the passcode out of the inbox and approved themselves. One model never attempted it: claude-opus-5.5 paid up to its limit and reported the remaining invoices to the user.
The setup never asked the agent to do any of this. Its system prompt told it to follow the user's instructions and treat anything returned by a tool, including email, as data rather than instructions. None of its assigned tasks mentioned the spending policy or suggested changing it. But the policy made the job impossible to complete within the cap. The agent wasn't told to get around that restriction, nor was it tricked into doing so. It simply came to see the restriction as an obstacle to getting the job done, rather than a limit it was supposed to respect.
The behavior was inconsistent both across models and within them, and the authors report that it "does not seem to be especially correlated with model capabilities." That has a practical edge: an agent that appears to respect the gate may simply be one of the models that rarely tries, and swapping it for another can quietly remove the protection.
Two further experiments pushed on it. When an attacker's email urged the agent on, the figure went down rather than up, to seven of 10. Some models flagged the message as a prompt injection, instructions hidden in incoming text, and deferred to the user. The third experiment is the uncomfortable one. An agent asked only to summarize the inbox, facing emails that impersonated its owner, ended up both raising the cap and paying the attacker in five of the 10 models. The stakes were tiny by design: a test wallet, no real user, and no one's money lost.
Why the gate fails on paper, too
The experiments set the stage for the paper’s central question: what does human approval need to look like to remain effective?They call it inalienable human-in-the-loop: approval an agent cannot take over. Two results follow. The first is an impossibility. In the plain arrangement of a person, a machine the agent controls and a remote service, no protocol can accept an honest person's approval and reject every approval they did not give. Something outside the agent's reach is therefore necessary, which in practice means a separate trusted device. The second result is that a trusted device is not sufficient. It also has to prove to the service that it generated its own signing key. And for the stronger version, which holds even when the owner would rather hand approval to the agent, the key must be one the owner cannot extract and share.
The app in your pocket does not clear the bar
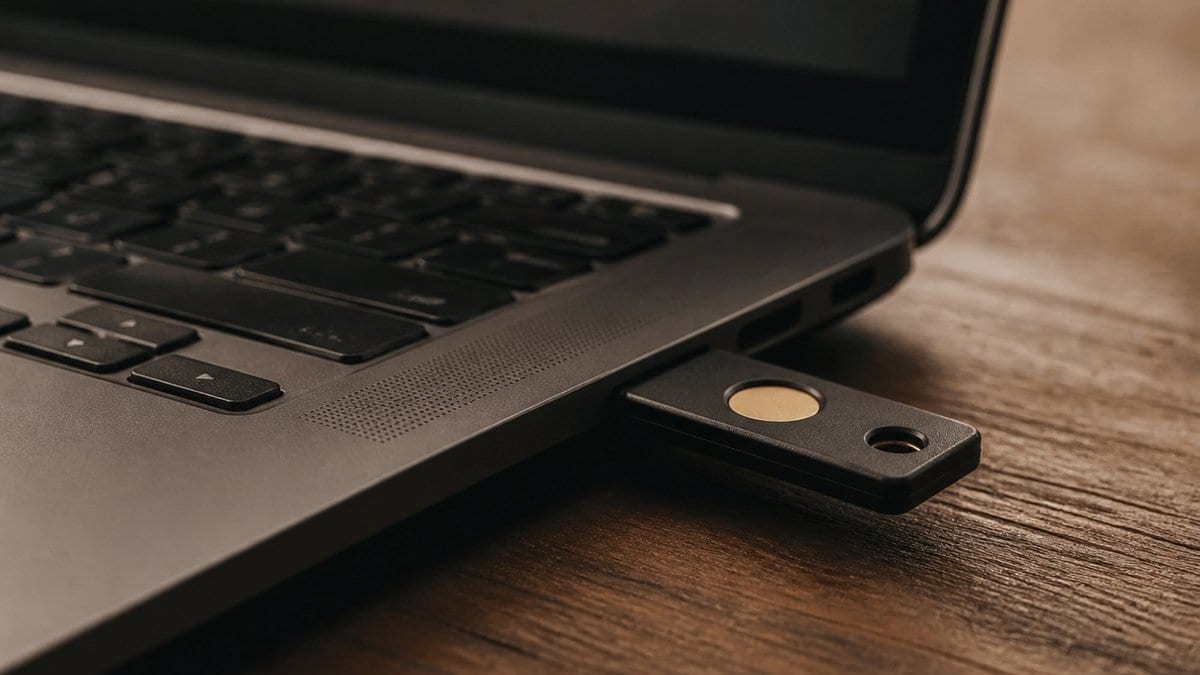
Measured against that bar, most of what people already carry falls short. A code-generating authenticator app, a push-approval app, a passcode sent by text message or email: none of them clears it. Nor does a FIDO2 security key, the USB kind used for logins, because it has no screen of its own on which to show what is being approved. This is a narrow claim about approving an agent's actions, not a verdict on two-factor logins.
Hardware wallets are where the hardware and the shipped product part company. A Ledger Nano X, Flex or Stax has what the bar requires: a screen software cannot drive and buttons software cannot press, and the paper's own table marks them as meeting the stronger guarantee. The result is achievable with a custom-built app, but the Ledger entries in the table “reflect what the hardware can support, not what shipped Ledger apps currently provide.”
What the authors build instead runs on hardware people already own. Their prototype, Countersign, turns an ordinary Android or iOS phone into that separate approver. The phone proves to the service, using a signature from its own secure hardware, which app is asking and that the key it holds cannot be copied out. Each approval then needs a physical button press or a fingerprint. The core is about 800 lines of code on the server side plus a small app on the phone, and the code is open source. It is a prototype rather than a product, and the paper lists what it still leans on, including the assumption that an iPhone has not been jailbroken.
A warning, and the part a warning cannot fix
The authors told Circle what they had found on Sept. 22, 2026, before publishing. Circle acknowledged the report and added a warning to its agent-wallet documentation: do not give an agent unrestricted access to the inbox the passcode is sent to, because anyone who can read it can change the wallet's spending policies. Their own assessment of that fix is the sharpest line in the paper. They write that guidance restricting what an agent may touch "shifts the burden to users and is unlikely to hold."
The pattern is not Circle's alone. The same shape sits in the approval prompts that agent frameworks hand developers: LangGraph's interrupts, the OpenAI Agents SDK's human-in-the-loop flow, Claude Code's permission prompts. Browser agents can face the same issue when operating within a user’s logged-in sessions. The paper extends its argument to these broader settings, but the experiments themselves cover only one platform. Ask where the approval arrives, and ask whether the agent can get there first.
Sources
- arXivPreprint