Google Bans a TV Box Maker It Says Built a Backdoor Into Its Own Devices
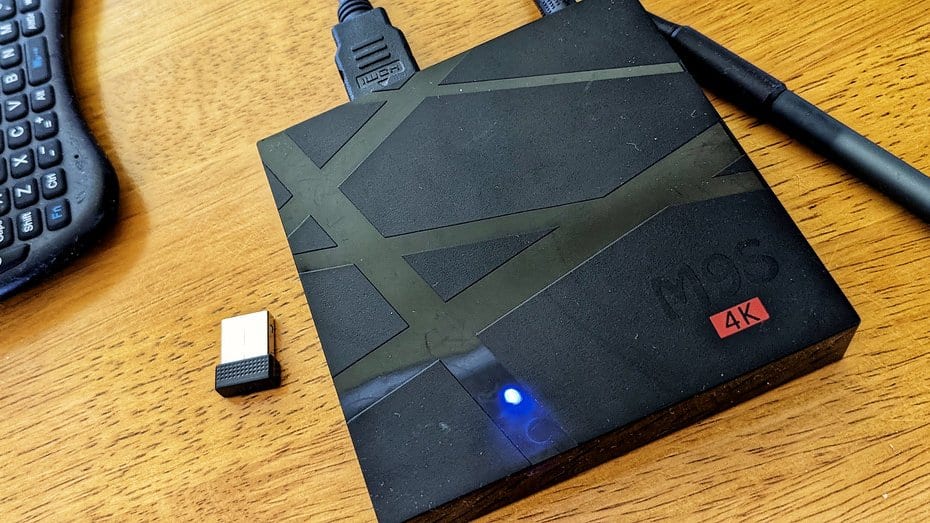
Google says it has shut down a backdoor that shipped inside more than 1.3 million Android TV set-top boxes, and has barred the manufacturer it blames from building certified Android devices again. Google Threat Intelligence Group, which published the account Nov. 2, 2026, said Google and industry partners dismantled the backdoor, which it calls XCPE, and that it had enrolled those boxes into a botnet.
For the owners of those boxes, what changes is that the machinery used to command them is gone. Google said it took legal action to take down the domains and servers used to control the botnet and install software on it, along with the control domains of the other malware families loaded through the backdoor.
Google said in its report that it assesses with high confidence that the backdoor and the botnet were developed, deployed and operated for financial gain by Videostrong Technology Co., an Android device manufacturer. That is Google's own assessment, from the company that runs the Android certification program and took the action. Google said that the code was built into many models and brands over several years, that Videostrong sold access to criminal affiliates, and that those affiliates' software ran advertising fraud, silently routed other people's internet traffic through the boxes and installed further malware.
Google said it has banned Videostrong and any future subsidiaries or affiliates from building and selling certified Android devices or supplying software to other certified vendors, and has cut the company off from shipping devices with Google apps preloaded. It said the maker got around Google's compatibility and security tests by loading the malicious code only after a device's first boot, and that it has since changed that review process and is tightening firmware checks on certified Android TV devices.
Google said that most of the infected machines were set-top boxes, but that it also found the malware on other Android devices, including telehealth equipment, karaoke machines and digital signage. It named Japan's National Police Agency, Lumen, HUMAN Security, Plume, Synthient and TrendAI as partners in the work.