Moving to a New Phone Left the Transfer Open to an Eavesdropper Nearby
The half hour at the phone shop counter is the dullest part of buying a new phone, and the most revealing. The old handset and the new one sit side by side while a progress bar crawls, and almost everything on one device walks across to the other. Contacts, call logs, photos, documents, app data, saved passwords. Six researchers in Graz set out to find who else could watch that walk.
Somebody standing nearby with cheap equipment could, it turns out. Florian Draschbacher, Stefan Mangard and four colleagues took apart the data transfer apps of seven Android makers: Google's Android Switch, Samsung's Smart Switch, vivo's EasyShare, Xiaomi's Mi Mover, OPPO's Clone Phone, Huawei's Phone Clone and Honor's Device Clone. They work at the Institute of Information Security at Graz University of Technology and at A-SIT Austria, the country's Secure Information Technology Center. Their analysis found what the paper calls "severe security vulnerabilities in all tools". All seven of them. The paper was presented in September at ESORICS, a European computer security conference, and the peer-reviewed version went online Oct. 7, 2026.
The eavesdropped data, in the paper's list, amounted to communication records, personal media and documents, and login credentials, which the authors call "a sizable dump of a user's digital life". The university's own account of the work goes further and says the team pulled health data and the credentials for saved Wi-Fi networks as well.
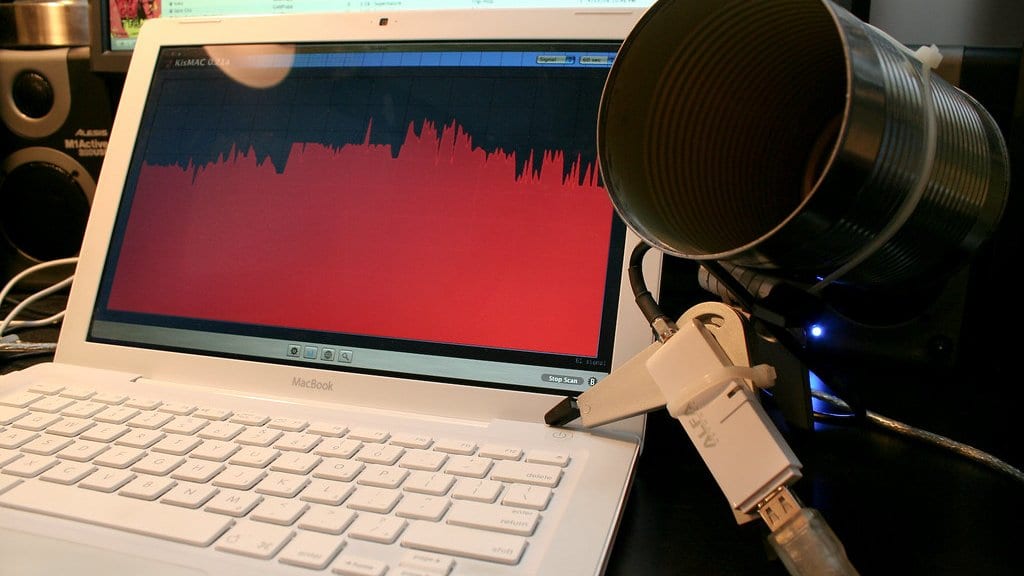
What that took is worth being exact about, because it decides whether any of this ever came near you. A transfer had to be actually running. The eavesdropper had to be within radio range of the two handsets, which Graz University of Technology puts at roughly 20 to 45 meters indoors, carrying cheap off-the-shelf equipment that cost the team less than 100 euros to assemble. Nothing else was required. No membership of your home or office network, no password, no hands on either phone, and nothing remote over the internet. Proximity was necessary but not sufficient: a passer-by holding an ordinary phone could not read your transfer.
The reason the handoff is the weak point is that the phones build the channel themselves. A migration app does not route your life through a company server. It stands up a direct Wi-Fi connection between the old handset and the new one, which is fast, works in a shop with bad reception, and costs the manufacturer nothing to run. That private link between two devices was the exposed one. "Because these apps are already preinstalled and very convenient for moving data to a new phone, these security gaps have an enormous impact," Draschbacher said in the university's announcement, in remarks translated from German.
Eavesdropping was the floor. Five of the seven apps were also open to data injection, which let someone in radio range run code on a phone that had just been set up. Three were vulnerable to extraction or injection by a local attacker, a narrower case that needs something already running on the device and a user who taps to approve it. The two should not be blended. The first is a stranger across the room; the second is already inside.
The apps are not niche. The seven have more than 12 billion downloads between them, a figure the authors counted from Google Play and Huawei AppGallery listings. It is a running total of downloads, not a count of people, phones or active installations. What makes it so large is that these tools arrive preinstalled on most Android phones, which is also what made the exposure wide: the app is simply there, on the new device, at the moment you want it.
The team told the makers before it told anyone else. That has produced eight CVE identifiers so far, the industry's public flaw records. Five are rated high severity and three medium, and none is rated critical. They came from four of the seven makers rather than from all of them: five from Samsung, and one each from OPPO, vivo and Huawei.
Those four have published fixes with version numbers attached. Samsung patched Smart Switch in the updates listed in its security bulletins for October and November 2025, crediting Florian Draschbacher and Rene Denifl by name. vivo's advisory names EasyShare 7.0.11.5 as the fixed version. OPPO's fix sits in ColorOS releases above 15.0.2, and Huawei's went out in its January 2026 bulletin.
Google, Xiaomi and Honor are the other three, and their side of the ledger is thinner. The paper's own footnotes record that the CVEs promised by Google and Xiaomi were still pending when the manuscript was finished, and that Honor did not acknowledge one of the scenarios. None of the three has published a security advisory of its own about the problem. The claim that all seven makers have now released updates comes from Graz University of Technology, on Oct. 15, 2026, and from no vendor's own advisory. One more footnote belongs beside it: OPPO could not reproduce one scenario despite the researchers' proof of concept.
The advice that follows is the researchers' own, and it is unglamorous. Before moving data between two phones, install the newest version of the migration app on both devices, along with all relevant updates, which in some cases means updating the whole operating system. It is the sort of instruction that is easy to skip in a shop with a queue behind you. It is also the step that closes the window.